On 21 September, a member of staff at a Baltimore hospital put a spreadsheet into an AI chatbot. The spreadsheet held the medical details of 3,182 patients. Nothing was hacked. Nobody broke in.
What happened at Johns Hopkins Bayview
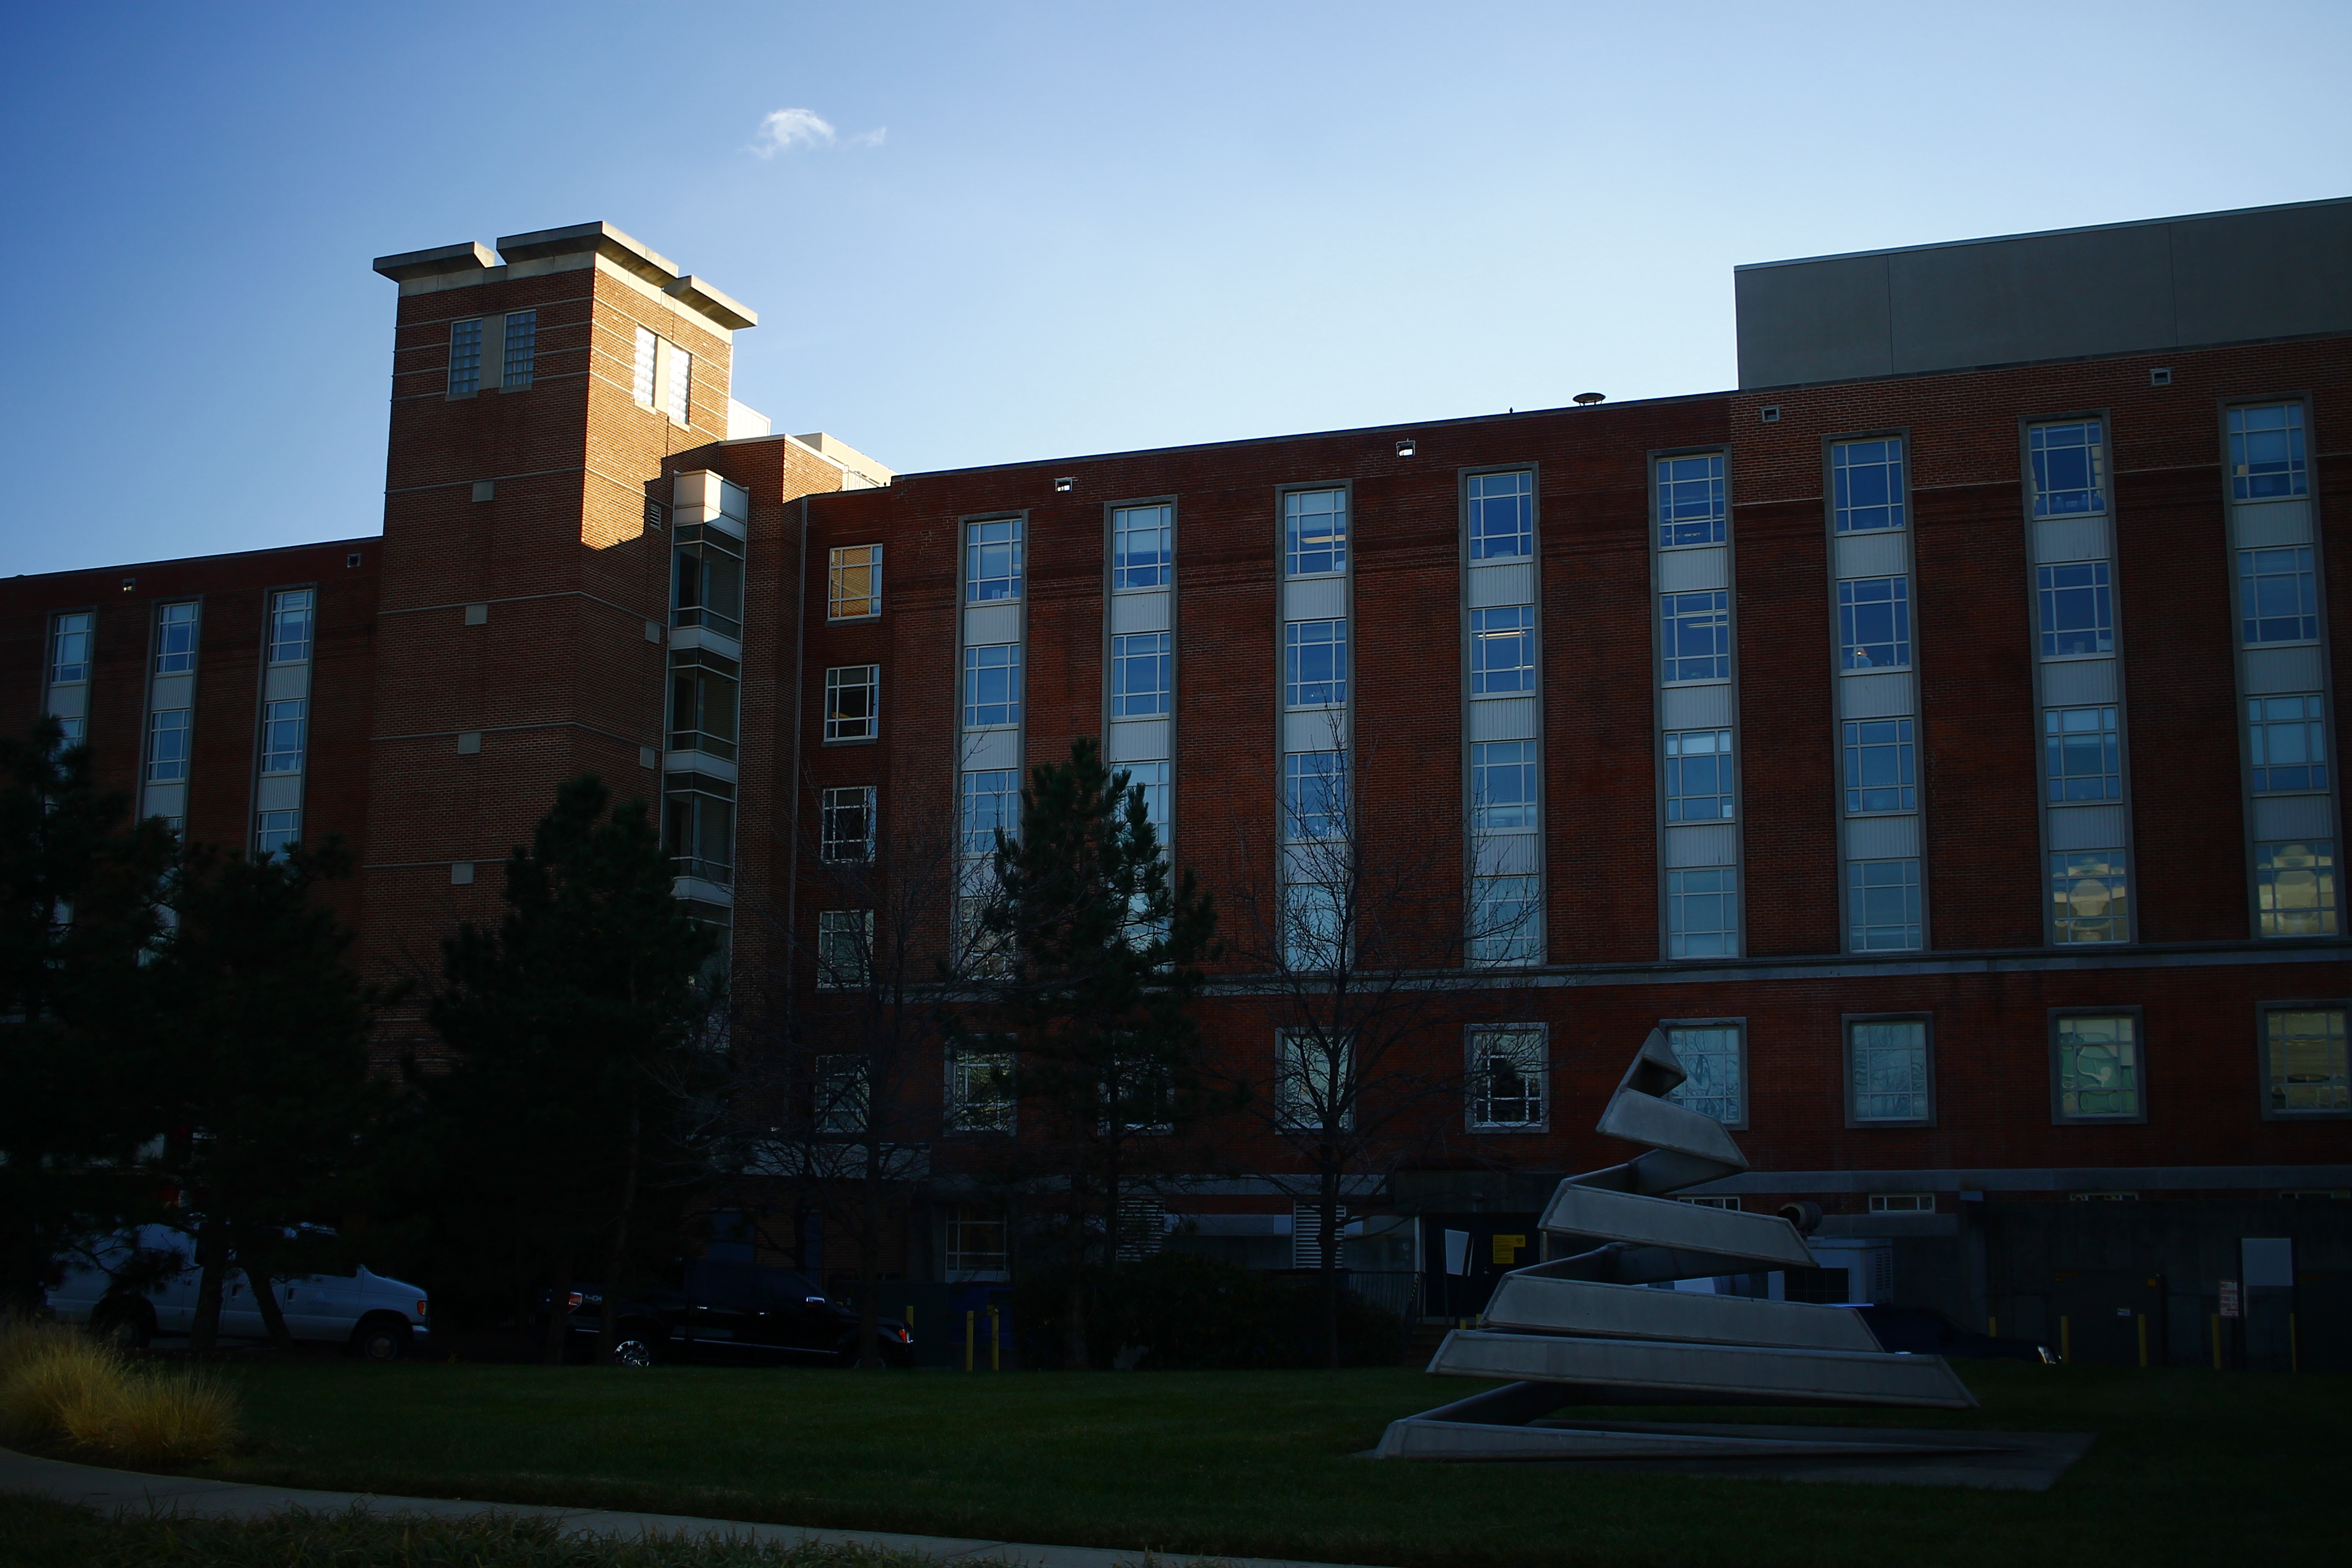
The hospital is Johns Hopkins Bayview Medical Center, in Baltimore, in the United States. On 21 September, during an internal review, an employee uploaded a spreadsheet of patient information to an AI tool the hospital had not approved for that use. The hospital has not named the tool.
The spreadsheet covered people admitted and treated between May and September 2026. It held their names, the dates they were admitted, the treatment they received, their medical record numbers, their account numbers, the department that treated them, the medications they were given, and the names of their doctors.
It did not hold Social Security numbers or bank details, the hospital said. That is the one piece of luck in the story.
The employee deleted the question, the conversation and the document from the tool’s history. The hospital also asked the company that runs the AI tool to delete the data. Letters went out on 22 October, offering 12 months of free credit monitoring through Experian IdentityWorks, and the hospital opened a phone line for patients with questions.
Why a chatbot is not a private drawer
A chatbot is not a drawer you close. It is closer to asking a stranger at a bus stop to read a letter for you: to get the help, you have to hand the letter over first.
When you type into one of these tools, the text leaves your computer and travels to a company’s servers — powerful computers in a building you will never visit. The answer comes back to your screen. The question stays with them.
Most tools now offer a setting to stop your conversations being used to train future versions of the product. That is worth switching on. It reduces what is kept. It does not make the tool private, and it cannot un-send a file you have already handed over.
Why it matters to you
You may never work in a hospital. The same mistake happens in offices, schools, letting agents, tax advisers and small businesses every week. Someone is behind on a task, an AI tool offers to help, and a real list of real people goes into the box.
Your name, the date you were admitted and the medicine you take are enough to build a story about you. Anyone who knows you were in hospital in July, and what you were treated for, can write an email that sounds like it came from your clinic.
That is how leaked records turn into phone calls. The caller knows too much to be a stranger, so you answer the questions.
And you will usually hear about it late. The hospital found this on the day it happened. Patients were told a month later.
What you can do
- Before you paste, take the names out. Replace a real name with “Patient A” or “Customer 1”. The tool can still help you with the shape of your table or the wording of your letter.
- Ask yourself whose file it is. A patient, a pupil, a customer, a colleague. Their permission is not yours to give.
- Use the tool your workplace has approved. If you do not know which one that is, ask before you paste, not after.
- Check the settings. In ChatGPT, open Settings and look for Data controls; in other tools, look for something called improve the model or model training, and switch it off. Delete old conversations you no longer need.
- If you have already pasted something you should not have, delete the conversation and then tell the organisation that owns the information. Speed matters more than embarrassment.
- Treat a breach letter as real, but call the number on the organisation’s own website, not the one printed in the letter. Fake breach letters are their own small industry.
Common misunderstandings
Myth: the AI forgets, because it says so
A chat history is a record. Deleting it removes it from your view and asks the company to remove it from theirs. That is a request, not an undo button, and copies can already sit in backups.
Myth: only passwords matter
Names, dates, record numbers and medications are not secret in the way a password is. In one way they are worse: you cannot change them. A password can be reset in a minute. The date you were admitted cannot.
Myth: this is a big company problem, not mine
It was one person and one spreadsheet. The hospital had policies, training and an approved list of tools, and the file went in anyway. What protects people is the habit of stripping names before pasting, not the policy on the wall.
What to watch for next
Expect more notices like this one, from hospitals, schools, insurers and employers, and expect them to arrive quietly. Most of them will not be a break-in in the sense we imagine when we hear the word hack.
Watch for the second wave: emails and calls that quote the leaked details back at you. A message that knows your clinic, your department and the month you were treated proves only that a list exists somewhere.
The one thing to remember
An AI chatbot is a conversation with a company, not a note to yourself. Before you paste, look at the list and ask whose names are in it.
If the answer is someone else’s, take them out first.
Image credit: Johns Hopkins Bayview Medical Center by Bohemian Baltimore, CC BY-SA 4.0, via Wikimedia Commons.